By Gertjan Bouwers, Senior Policy Adviser on Digital Identity, Ministry of the Interior and Kingdom Relations of the Netherlands.
By the end of 2026, European Union Member States must make at least one certified European Digital Identity Wallet available to their citizens. Much of the necessary technology is already in place. The far greater challenge will be convincing people to use the wallet and ensuring that public authorities and businesses trust the data it contains.
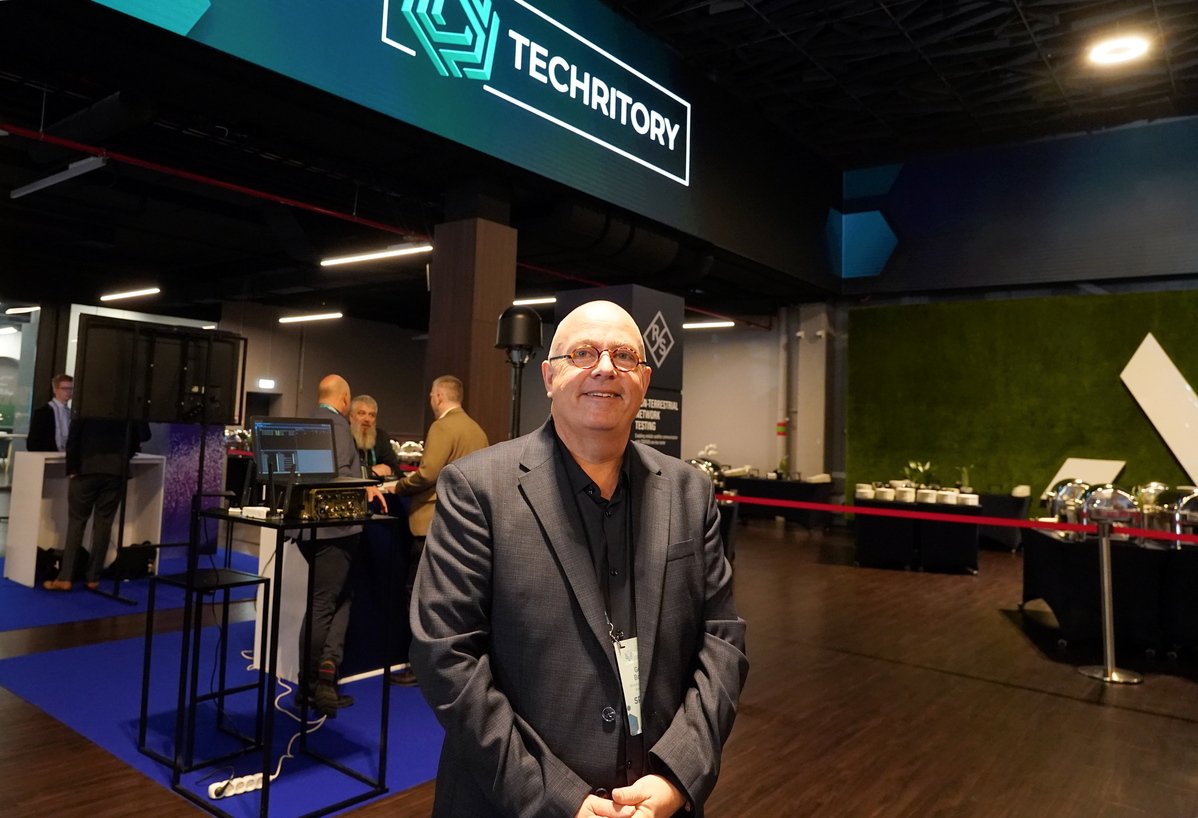
We discussed these issues in Riga during the Techritory 2026 panel discussion “Europe’s Digital Identity Reality Check”. Together with representatives of the European Commission, Latvia, Estonia and the technology sector, we examined how Europe is moving from developing regulations to practical implementation, and how to encourage people to actually use the new wallets.
The views expressed here are my personal professional opinions, based on my experience in developing digital identity policy in the Netherlands, and do not represent the official position of the Dutch government.
An ambitious goal and a tight implementation deadline
The promise of the European Digital Identity Wallet (EUDIW) to citizens is straightforward. It will enable people to identify and authenticate themselves both online and in person, when accessing public and private sector services, in their own country and elsewhere in Europe. The regulatory framework requires these wallets to be made available to citizens by the end of this year. In my view, this is a highly ambitious goal.
However, the biggest challenge is not technology. All the technological solutions needed to build such a wallet are already available. Some technical details still need to be refined, but the underlying technology is essentially ready. What is much more difficult is identifying trustworthy data sources that will issue digital credentials to the wallet, ensuring that service providers (relying parties) can trust and accept those credentials, and, most importantly, finding citizens who will actually want to use them.
All of this must also be achieved within a framework of supervision and certification. The main challenge, therefore, is not technology but building a trustworthy system.
There is a Dutch saying: trust arrives on foot but leaves on horseback. It is difficult to earn and easy to lose. That is why our biggest question is how to maintain citizens’ interest and demonstrate real added value, both in domestic and cross-border services. To accelerate implementation, the most important issue is understanding how credential issuers will connect their systems to the wallet. It is not the application itself.
Putting control over data in people’s hands
The greatest benefit for citizens is that they can control their own data. Today, much data is exchanged between organisations on a legal basis, but individuals often have little visibility of it. With the wallet, people can present their data directly to different organisations and share only what they choose to share.
An important element is the registration of service providers. To request data from a wallet, a service provider must be registered, specifying what data it requests and for what purpose. If a problem arises, it is always possible to check whether the registration is correct or whether something is wrong. This makes the system more transparent and accountable.
Latvia and the Netherlands face a similar situation. Both countries have made considerable progress with electronic identification systems. In the Netherlands, we have a highly trusted eID environment that is widely used. This year, we have already passed the milestone of one million cross-border authentications.
Citizens will therefore quite reasonably ask: why do I need a wallet if eID already works? If we can demonstrate and explain that the wallet is a genuinely useful addition to existing eID systems, people will have a reason to use it.
The answer must be very practical. Take the European Health Insurance Card, for example. I always have to remember to bring it when travelling abroad. Fortunately, I have rarely needed to use it. But when you do need it, it is extremely convenient to have it available in your personal wallet.
Verifying diplomas without weeks of waiting
In my view, the benefits for governments and businesses must ultimately translate into benefits for citizens.
For example, when you approach a service provider and need to present a diploma, you expect the competent authority to provide the service on that basis. A responsible authority will verify whether the diploma actually belongs to you and whether it was issued in accordance with the relevant rules. That takes time.
In Europe, the Internal Market Information System (IMI) is used for such checks. Cross-border verification of a diploma’s authenticity through this system can take a couple of weeks.
If the diploma is available in the wallet and supported by a qualified or public-body electronic attestation of attributes, the authority can recognise it much more quickly, without a wait of a couple of weeks. The process becomes faster for the citizen, while the authority can rely on the data it receives.
But this brings us back to trust. The authority must be confident in the authenticity and reliability of the data contained in the wallet.
Security and privacy do not have to conflict
People often ask how to strike a balance between convenient digital identification, personal data protection and cybersecurity.
In my view, these objectives should not be presented as competing priorities. Doing so creates the impression that we have to choose one over another. If the wallet is designed with great care, these objectives can reinforce each other.
Three elements underpin this approach. First, under the amended implementing regulations, a registration certificate for the service provider is mandatory. Second, selective disclosure allows users to share only the data necessary in a particular situation. Third, data is stored in a decentralised manner. Together, these elements allow people to share only what they want, and only with those they choose.
For countries developing their own wallets, I recommend looking at Annex I of Commission Implementing Regulation (EU) 2024/2981 on wallet certification. It sets out the identified security and privacy risks that must be taken into account when developing national certification schemes. If a national certification scheme convincingly addresses all these risks, such a wallet deserves users’ trust.
In the Netherlands, we are currently identifying the amendments needed to our national legislation. We plan to submit them for public consultation and then to parliament next year.
Dutch national law must establish a legal basis for the registration of service providers. A legal basis is also needed for issuing person identification data into the wallet so that Dutch citizens can start using it. This is currently one of the most challenging deadlines. I do not know whether the same applies to Latvia, but these are issues worth examining well in advance.
A common foundation, different digital wallets
The Netherlands explicitly aims to allow private wallets within its national framework alongside the government wallet it is developing, giving citizens a choice.
Our principle is simple: “Diversity at the front end, uniformity at the back end”. The user experience may vary, but the underlying technical framework must be strong and trustworthy.
By creating a framework in which wallets can evolve and opening it up to private initiatives, we will also create opportunities for different sectors to develop their own solutions. For example, the healthcare sector could use the common framework to build solutions tailored to its needs. If private companies develop sector-specific solutions for their communities, trust will eventually grow in the framework and in the solutions built within it.
After all, trust does not come from regulation. It comes from use, when people actually use the wallet and experience its benefits.
In my view, Europe is definitely moving in the right direction by strengthening its position in relation to global players – large companies whose standards differ from European standards. Common compliance requirements across the Union, for example for trust services and wallets, help us preserve European values and maintain independence from standards set by global technology companies.
In Europe, this always takes a great deal of time. But if we do not start today, it will take even longer in the end. I believe that by acting now, we can build a well-functioning digital identity ecosystem in Europe within five to ten years. If we postpone this work, it could take as long as 15 to 20 years.
As Voltaire put it, the perfect is the enemy of the good. There is no perfect moment to begin, and delaying action only pushes the result further away. We should therefore not wait for the right moment or for technology to be completely ready. We need to build a trustworthy framework, involve credential issuers and service providers, and offer people tangible benefits. Only then will the European Digital Identity Wallet become an everyday tool rather than just another app on people’s phones.